


Key Takeaways
- A newly disclosed Bitcoin Core vulnerability raises recent questions in regards to the resilience of crucial community infrastructure.
- Synthetic intelligence is uncovering safety weaknesses that escaped years of typical software program scrutiny.
- The rising sophistication of automated vulnerability analysis is forcing cryptocurrency builders to rethink how shortly safety threats are addressed.
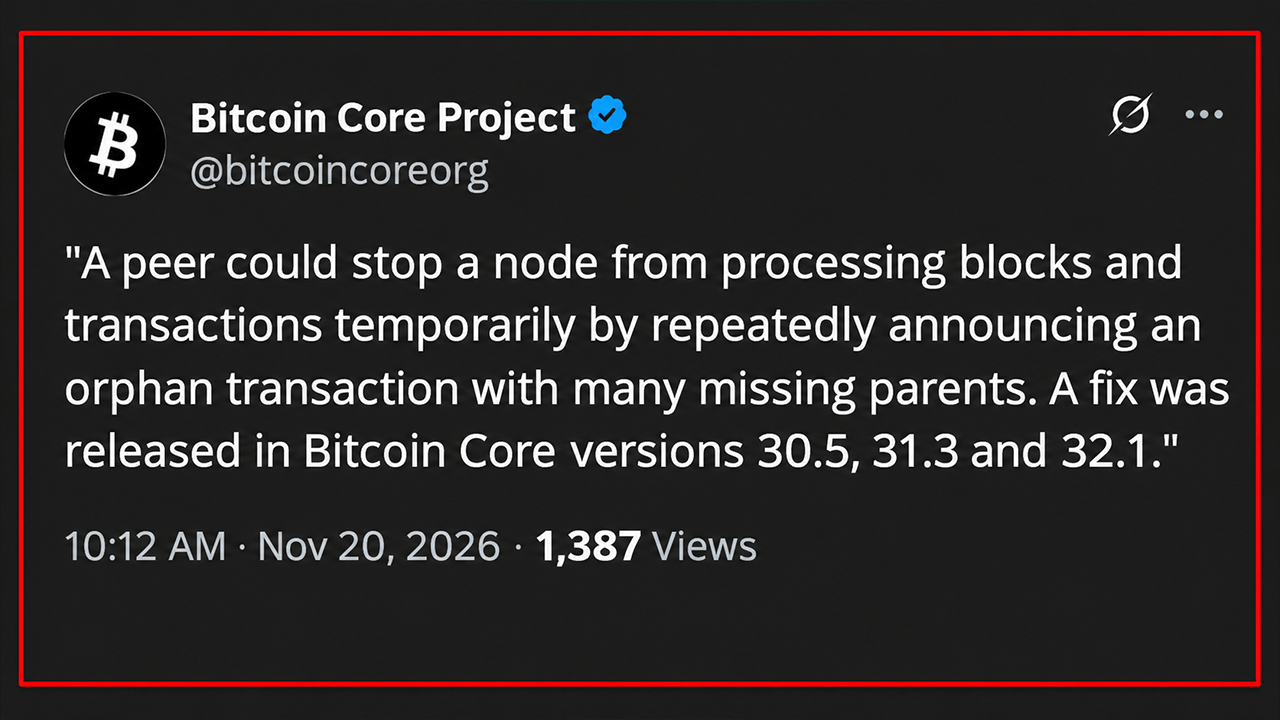
The vulnerability, cataloged as CVE-2026-117348 and titled “Node stall by duplicate orphan bulletins,” may stop affected Bitcoin nodes from processing incoming blocks and transactions for greater than a dozen seconds per malicious message.
In line with the official Bitcoin Core disclosure, the issue affected variations 29.0 by 29.5, 30.0 by 30.4, and 31.0 by 31.2. Corrective updates can be found in variations 30.5, 31.3, and 32.1, whereas the discontinued 29.x department will obtain no additional patches.
How an AI Scanner Uncovered Bitcoin Core’s Node-Stalling Vulnerability
The software program growth group referred to as Bitcoin Core maintains a brief holding space referred to as the “orphanage,” the place transactions await lacking mother or father transactions. When one other community participant broadcasts one in every of these transactions, the software program examines its dependencies to find out which lacking data ought to be requested.
The vulnerability exploited an ignored inefficiency in that course of. Bitcoin stock messages can comprise 50,000 entries, but the software program didn’t disregard duplicate transaction bulletins. An attacker may repeatedly reference an orphan transaction with hundreds of lacking dad and mom, forcing the receiving node to carry out the identical computationally costly checks hundreds of occasions.
Every manipulated message may stall processing for greater than 12 seconds, leaving the focused node briefly unable to deal with incoming blocks or different community communications.
The invention originated with Undertaking Loupe, an automatic massive language mannequin (LLM) safety initiative developed by Elias Rohrer at Spiral, Block’s open-source Bitcoin growth division. Bitcoin Core developer Gregory Sanders subsequently validated the discovering and introduced it to the undertaking’s safety group.
Undertaking Loupe reported the vulnerability on July 8. An impartial researcher recognized as Stutxo submitted a separate report on Aug. 4, the identical day Sanders opened a corrective pull request. Builders merged the repair on Aug. 6, and Bitcoin Core 32.1 included it on Oct. 27.
The Nov. 20 disclosure accompanied up to date releases for maintained older branches. The correction ensures every distinctive transaction announcement is processed solely as soon as per stock message.
Though the flaw permitted non permanent denial-of-service assaults, the advisory didn’t set up any mechanism for stealing bitcoin or completely damaging nodes.
AI Safety Analysis Exposes Lengthy-Standing Blockchain Weaknesses
The disclosure arrives amid a rare 12 months for AI-assisted vulnerability analysis throughout cryptocurrency infrastructure.
In February, an AI-assisted assessment recognized a crucial signature-verification weak point within the XRP Ledger’s proposed Batch modification earlier than activation. One other investigation uncovered a high-severity vulnerability in Nethermind, an Ethereum execution consumer, probably affecting validator operations.
By late Could, researcher Taylor Hornby had used an AI-assisted auditing system to establish a four-year-old flaw in Zcash’s Orchard privateness protocol. The vulnerability may have permitted undetectable counterfeit ZEC, though builders corrected it earlier than public disclosure.
August introduced one other putting demonstration. Sixteen volunteer builders taking part in a Bitcoin safety initiative generated 4,962 findings throughout 390 initiatives in roughly in the future, together with 85 initially categorized as crucial.
Nonetheless, automated discovery launched appreciable problems. Maintainers confronted hundreds of experiences requiring human verification, whereas professional safety issues competed with false positives and poorly substantiated findings.
Core Lightning builders additionally confronted an inflow of AI-generated vulnerability experiences, in the end figuring out real safety issues requiring corrective releases.
The implications prolong past defensive analysis. Safety specialists have raised issues that malicious actors can make use of related know-how to uncover weaknesses in older software program, probably shortening the helpful lifespan of conventional safety audits.
Bitcoin Core Accelerates Disclosure as AI Adjustments Safety Analysis
Recognizing this growth, Bitcoin Core revised its vulnerability disclosure coverage in October. Points categorized as simply discoverable, together with weaknesses identifiable by comparatively easy LLM-assisted evaluation, now obtain accelerated public disclosure alongside corrective releases.
CVE-2026-117348 illustrates that method in apply.
The episode additionally exposes a tough safety paradox. AI can establish ignored vulnerabilities quicker than typical analysis, however its rising accessibility probably offers attackers comparable capabilities. For open-source cryptocurrency infrastructure, the central problem is more and more not merely discovering weaknesses, however validating and correcting them earlier than adversaries exploit the identical information.


