What turns a compliance overview from a doc chase into a transparent choice course of? A channel compliance audit guidelines brings the work right into a constant sequence: outline the scope and standards, assign duties, collect and assess proof, report findings, and monitor corrective actions. Tailor the guidelines to the necessities and dangers related to the group and its channel relationships.
A guidelines could make opinions extra constant, however solely when every merchandise has clear possession and supporting documentation. Set up insurance policies, transaction data, accomplice data, and management proof so reviewers can see what was assessed and the place follow-up is required.
This information explains what to incorporate, tips on how to assign duties, and tips on how to overview documentation with out dropping sight of the audit’s goal. It additionally covers tips on how to report findings and talk their impression and subsequent steps to management, so the overview helps choices relatively than changing into a disconnected record of points.
Key Takeaways
- Set a documentation overview cadence that responds to modifications in methods, distributors, and relevant necessities.
- Outline the audit’s scope round related obligations, channel processes, and danger areas earlier than gathering proof.
- Assign clear possession for proof assortment, management overview, and incident response throughout groups.
- Translate findings into prioritized actions so management can see publicity, accountability, and progress.
- Use structured channel knowledge administration to assist extra constant opinions of accomplice exercise, offers, and incentives.
How usually ought to compliance documentation be reviewed?
Assessment compliance documentation on a daily schedule, usually yearly, and at any time when methods, distributors, or relevant necessities change. A brand new partner-data workflow, platform integration, or revised coverage could make present proof incomplete. Assign an proprietor to every overview set off, report the date, and replace the audit calendar so modifications are addressed earlier than the subsequent scheduled cycle.
Use danger to set the depth and timing of every overview. For instance, a course of involving delicate data may have nearer monitoring than a secure administrative process. Examine present insurance policies with precise practices, then doc gaps, house owners, and remediation steps. The NIST Cybersecurity Framework 2.0 features a Govern operate protecting cybersecurity danger technique, expectations, and coverage, in accordance with the Nationwide Institute of Requirements and Expertise.
Administrative safeguards want proof, not simply coverage titles. Maintain accepted insurance policies, entry procedures, position assignments, coaching data, and incident-response procedures collectively. The Honest Labor Requirements Act (FLSA) of 1938 establishes U.S. requirements for minimal wage, time beyond regulation compensation, hours labored, and recordkeeping, in accordance with the U.S. Division of Labor. The place these data apply, embody the related timekeeping and recordkeeping procedures within the overview scope.
Put together paperwork in a repeatable sequence. First, determine the regulation, contractual obligation, or inner management underneath overview. Then collect the present coverage, supporting data, prior findings, and proof that controls function as described. In keeping with the U.S. Division of Well being and Human Providers, HIPAA audits assess whether or not healthcare suppliers, well being plans, and different entities adjust to privateness and safety guidelines defending affected person data.
Management doc variations by recording an proprietor, approval standing, efficient date, and revision historical past. Take away out of date copies from energetic workspaces whereas preserving data underneath the group’s retention schedule. Clearly distinguish draft insurance policies from accepted insurance policies so reviewers can determine which procedures are formally in power.
Schedule opinions of coaching data, too. Match completion proof to the coverage or process taught, and report follow-up when employees want further instruction. When a course of modifications, replace its supplies and assign coaching to affected roles. These steps assist present whether or not workers obtained related steering and whether or not documentation displays present operations.
For a channel compliance audit guidelines, join every overview merchandise to its proof, proprietor, and subsequent overview set off. GDPR non-compliance can lead to fines of as much as 4% of annual international turnover, in accordance with the European Union. That makes requirement monitoring and documented updates necessary elements of a disciplined overview course of.
What Is a Compliance Audit Guidelines?
A channel compliance audit guidelines is a structured set of questions and proof requests for assessing whether or not a corporation follows relevant necessities. It turns obligations into reviewable gadgets, resembling whether or not a accomplice settlement is present, gross sales data assist reported transactions, or a required approval is documented. Every merchandise ought to determine the management being examined and the proof that may reveal the way it works.
Outline what the audit covers, which places or enterprise processes are included, and the interval represented by the proof. For a channel overview, the scope would possibly embody accomplice onboarding, deal registration, incentive claims, advertising approvals, and gross sales reporting. State exclusions as properly, so management can distinguish reviewed areas from processes outdoors the evaluation.
Relevant necessities rely upon the group’s actions, contracts, markets, and knowledge practices. A overview would possibly map inner procedures to contractual phrases, privateness obligations, or monetary controls, and report the supply for every requirement. For instance, a corporation dealing with private knowledge linked to EU residents might assess related GDPR controls, whereas a monetary reporting overview might contemplate SOX necessities. For firms managing channel operations throughout a number of jurisdictions such because the EU and US, consulting cross-border tax and regulatory advisory companies like cidatax.it could assist make clear advanced regional compliance obligations.
Use danger elements to find out which controls deserve nearer testing. Assess data sensitivity, transaction worth, entry permissions, accomplice dependencies, and the historical past of unresolved findings. A accomplice with entry to confidential buyer data might warrant completely different proof checks from a accomplice utilizing accepted public advertising supplies. File the rationale so audit actions comply with a constant danger foundation.
To audit accomplice gross sales practices, advertising claims, and model use, examine accomplice agreements and accepted supplies with sampled gross sales data, marketing campaign property, and public claims. Doc exceptions, supporting proof, and the accountable proprietor. Examples embody an unapproved product declare or outdated model art work.
In the course of the audit, reviewers can comply with an outlined sequence: affirm goals, map every requirement to a management, determine proof sources, take a look at a pattern, and report outcomes. Procedures ought to distinguish a lacking doc from a management failure. As an example, a lacking approval report requires follow-up on each the approval course of and its proof path.
A helpful guidelines hyperlinks each requirement to its danger, take a look at technique, proof, discovering, and corrective motion. That construction helps organizations see why a difficulty issues and what motion addresses it. For channel workflows, discover structured accomplice workflow administration as a option to convey associated data right into a extra constant course of.
Auditor roles and duties
Assign audit duties earlier than proof assortment begins. Inner audit groups can coordinate the overview, outline take a look at procedures, and doc outcomes. Exterior auditors or specialised compliance professionals might conduct the evaluation—just like how firms dealing with bodily distribution have interaction impartial companions like The Inspection Firm for high quality and course of audits—whereas regulatory groups present data and course of context. Clear possession helps forestall unanswered requests and duplicate testing.
Separate the work into outlined roles. The audit lead units goals, scope, and timelines; management house owners clarify how procedures function; proof coordinators gather data; and reviewers take a look at whether or not proof helps every management. For instance, a channel operations proprietor can clarify deal registration approvals, whereas finance provides transaction data. The auditor data the conclusion and supporting proof.
A shared accountability matrix makes handoffs seen. Listing every management or course of, the accountable proprietor, supporting groups, proof location, and escalation contact. For accomplice onboarding, the matrix would possibly assign operations to keep up approval data, IT to handle system entry, and authorized to interpret contract phrases. Assignments differ by program, so doc the precise workflow relatively than assuming each division has the identical duties.
Embody service suppliers within the matrix after they deal with methods, transactions, or delicate data. PCI DSS steering says organizations stay liable for overseeing service suppliers and monitoring every supplier’s PCI DSS compliance standing. Assign an inner proprietor to trace supplier proof, overview standing modifications, and report unresolved gaps. A contract alone doesn’t reveal ongoing oversight.
Assign clear house owners for incident and breach response. Establish who receives reviews, preserves related data, assesses operational impression, coordinates response steps, and informs management. For a suspected publicity involving accomplice knowledge, the response path ought to determine the system proprietor, safety contact, channel operations lead, and decision-maker. File incident timelines and actions in a constant case file.
Auditors ought to assess whether or not these duties work in observe. Hint a pattern incident from its preliminary report by means of investigation, choices, and closure, and examine timestamps and data throughout groups. If an alert has no assigned proprietor, doc the accountability hole and its impact on response coordination. This take a look at connects governance paperwork to operational habits.
Frontline employees can determine course of gaps that coverage house owners might miss. Interview related workers about accomplice approvals, advertising opinions, or knowledge handoffs. Distinguish employees observations from verified proof, then validate materials findings in opposition to system data or accepted procedures. This retains conclusions grounded and helps management assign corrective actions to the proper house owners.
Speaking audit findings to management
Channel compliance violations can result in monetary penalties, authorized motion, reputational injury, or lack of enterprise licenses. Penalties rely upon the requirement breached and the circumstances. Remediation ought to determine the trigger, assign an accountable proprietor, set a corrective motion, and monitor proof that the repair works.
Start the management report with the audit scope, overview interval, and general conclusion. Then summarize vital findings, affected processes, supporting proof, and choices wanted. For instance, if accomplice claims lack approval data, state which course of was sampled, what documentation was lacking, and who should tackle the management hole.
Assess every discovering by its potential impression, chance of recurrence, and attain throughout channel operations. A lacking report in a single transaction differs from a repeated approval failure throughout accomplice claims. Clarify the excellence with proof, resembling sampled information, system logs, or documented procedures, relatively than counting on labels like “excessive danger” with out context.
Frequent findings embody incomplete accomplice information, outdated procedures, inconsistent approval trails, and overdue corrective actions. Stop recurrence by figuring out why every concern occurred. If employees use an out of date kind, replace the managed template and take away outdated copies. If approvals are routinely absent, make clear the workflow and monitor accomplished data.
Observe corrective actions in a desk itemizing the discovering, root trigger, proprietor, due date, standing, and closure proof. This format helps management distinguish rapid containment from longer-term course of modifications. For instance, limit an incorrect declare whereas the accountable group corrects the underlying overview process and paperwork its approval.
Embody unresolved points and exterior dependencies within the report. If a service supplier controls related knowledge, state which proof stays excellent, who owns follow-up, and what choice management should make. PCI DSS oversight duties, for instance, make supplier standing related to organizations monitoring service-provider compliance.
Shut with a concise choice abstract: actions accomplished, assets or approvals wanted, and the subsequent monitoring level. Maintain supporting proof obtainable for audit follow-up, together with data exhibiting that corrective actions had been accomplished successfully. Documenting even minor points can reveal recurring patterns and assist management plan prevention throughout groups.
Compliance audit guidelines
Use this guidelines to conduct a channel overview from documented necessities by means of corrective actions. For each take a look at, report the requirement, proof examined, outcome, proprietor, and follow-up date. This construction creates accountability and makes ongoing monitoring simpler to keep up.
To examine accomplice pricing, low cost, and promotion compliance, examine accepted tariffs and marketing campaign phrases with sampled quotes, invoices, and claims. File every variance, its approval standing, and the coverage that governs it.
Audit reseller and distributor compliance by means of a repeatable sequence: outline the scope, choose companions and transactions, collect data, take a look at controls, doc exceptions, and assign remediation. For instance, hint a registered deal from submission by means of approval to its closing gross sales report.
Assess channel accomplice knowledge privateness and cybersecurity by reviewing entry permissions, data-handling procedures, safety insurance policies, incident plans, and related testing reviews. Examine documented controls with noticed system entry, and report gaps for accountable house owners.
- Affirm scope and necessities. Establish coated companions, processes, agreements, and relevant obligations earlier than testing begins.
- Map every requirement to a management. Hyperlink a contract time period or inner coverage to the process and proof that reveal compliance.
- Check accomplice authorization. Examine energetic reseller data with present agreements and accepted territories to determine mismatches.
- Hint monetary exercise. Match chosen transactions to accepted reductions, promotions, deal data, and supporting documentation.
- Assessment advertising and model controls. Examine accomplice marketing campaign supplies with accepted claims and present model property, then report exceptions.
- Look at knowledge entry. Examine accomplice roles with system permissions and documented approval data to determine extreme or outdated entry.
- Validate supplier oversight. File service-provider standing, proof reviewed, and the interior proprietor liable for follow-up.
- Doc every discovering. Seize proof, impression, root trigger, motion proprietor, due date, and closure standards in a managed report.
- Observe remediation and monitoring. Re-test accomplished actions and protect proof exhibiting whether or not the corrective management operates as supposed.
Software program can centralize accomplice data, approvals, and overview proof, lowering dependence on scattered information. A structured workflow additionally helps groups join a failed take a look at to its proprietor and follow-up. Discover a structured partner-management workflow to assist clearer audit trails.
Pc Market Analysis
Pc Market Analysis can assist when channel opinions expose fragmented accomplice data, deal exercise, or incentive knowledge. Its channel administration software program centralizes data linked to accomplice workflows, serving to organizations keep visibility throughout processes that assist oblique gross sales and advertising. That is helpful when guide monitoring makes it tough to find constant data or join exercise with supporting documentation.
PartnerPortal™ centralizes accomplice onboarding, deal registration, and efficiency monitoring. These workflows give groups an organized view of accomplice data and exercise. When an audit examines whether or not a deal was registered and tracked by means of the suitable course of, centralized data assist groups find related data and perceive how the workflow operates.
Pc Market Analysis gives Co-op/MDF Administration and Rebates & Incentives for administering channel program funds, claims, and incentive data. When a overview identifies disconnected data throughout program administration, gross sales, and finance, structured administration of those workflows can assist clearer operational visibility.
Deal Registration helps opinions of how partner-submitted alternatives are recorded and tracked. A constant course of helps groups comply with deal data by means of its workflow and join data to the related accomplice exercise. It doesn’t substitute a corporation’s audit standards, however helps the channel operations and knowledge processes these standards look at.
Take into account Pc Market Analysis when recurring overview work relies on spreadsheets, scattered information, or guide handoffs throughout channel groups. Its cloud-based SaaS options are designed to automate and streamline channel administration for international enterprises. The match relies on the workflows being administered, resembling accomplice onboarding, registered offers, co-op or MDF funds, and incentive applications.
Use audit findings to determine the place channel data wants extra constant administration. Repeated gaps in accomplice data might level to a workflow concern, whereas disconnected deal data might make exercise tougher to hint. A platform constructed for channel administration can assist groups set up these data and enhance knowledge visibility.
In case your overview factors to a necessity for extra structured channel knowledge and workflows, contact Pc Market Analysis to debate your necessities.
Put Your Assessment Course of Into Movement
A helpful channel compliance audit guidelines must be a part of ongoing channel operations, not a doc opened solely earlier than a overview. Assign a transparent proprietor to every follow-up, join findings to operational choices, and use recurring opinions to maintain duties seen as accomplice workflows evolve. This makes audit work an ongoing administration observe relatively than a disconnected train.
Begin by figuring out the place fragmented data or guide handoffs make accomplice exercise tougher to trace. A structured channel administration method can assist set up the information and workflows behind these opinions. Pc Market Analysis helps channel administration by means of options designed for accomplice and incentive processes.
Transfer ahead by aligning your overview priorities with the channel workflows that want clearer oversight. Discover the subsequent step with Pc Market Analysis, and hold constructing a overview course of that helps knowledgeable choices and stronger accountability.
Often Requested Questions
What’s a channel compliance audit?
A channel compliance audit evaluates whether or not partner-related actions comply with the group’s relevant necessities and documented controls. It might look at how a reseller is accepted, how gross sales transactions are recorded, or how advertising supplies are licensed. The overview ought to distinguish between a management that exists on paper and one that’s persistently adopted. Its scope relies on the group’s channel mannequin, related obligations, and danger areas.
What ought to a channel compliance audit guidelines embody?
Embody the requirement being examined, the channel course of it impacts, the proof wanted, the take a look at technique, and a spot to report the outcome. For instance, a reduction overview can examine an accepted promotion with chosen quotes and invoices. Add an proprietor and follow-up standing for exceptions. This construction helps reviewers distinguish a lacking report from a course of that didn’t function as supposed.
What data and paperwork must be reviewed in a channel audit?
Assessment accomplice agreements, onboarding data, approval histories, gross sales transactions, promotion phrases, and advertising supplies related to the audit scope. For knowledge or safety opinions, embody entry data, privateness and safety procedures, incident response plans, and relevant third-party agreements. The proof wanted relies on the management being examined. Match every doc to its proprietor and the accomplice exercise it helps.
What U.S. legal guidelines and rules apply to channel companions and resellers?
Relevant necessities rely upon the group’s actions, data, and contractual relationships. Examples embody the Honest Labor Requirements Act for related wage, time beyond regulation, hours-worked, and recordkeeping practices; HIPAA for coated healthcare entities dealing with protected affected person data; and SOX for relevant monetary controls. Office well being and security necessities may additionally matter. A accomplice overview ought to determine which obligations apply to the precise course of, relatively than assume each rule covers each reseller.
What are frequent channel compliance dangers and crimson flags?
Look ahead to unexplained pricing variations, promotions with out clear approval, incomplete accomplice information, inconsistent gross sales data, and advertising claims that differ from accepted supplies. For instance, a reseller’s bill might present a reduction that doesn’t match the promotion phrases. Repeated guide corrections or unresolved exceptions can sign weak course of controls. Assess every concern in opposition to its proof, potential impression, and recurrence earlier than assigning corrective motion.
How usually ought to channel compliance audits be carried out?
Set a predictable audit schedule, then add opinions when materials modifications have an effect on channel operations. Examples embody introducing a brand new accomplice workflow, altering an information system, revising an settlement, or responding to a management failure. Organizations generally conduct compliance audits yearly or bi-annually, whereas higher-risk environments may have extra frequent opinions. Align timing with relevant necessities and the tempo of operational change.
Article by
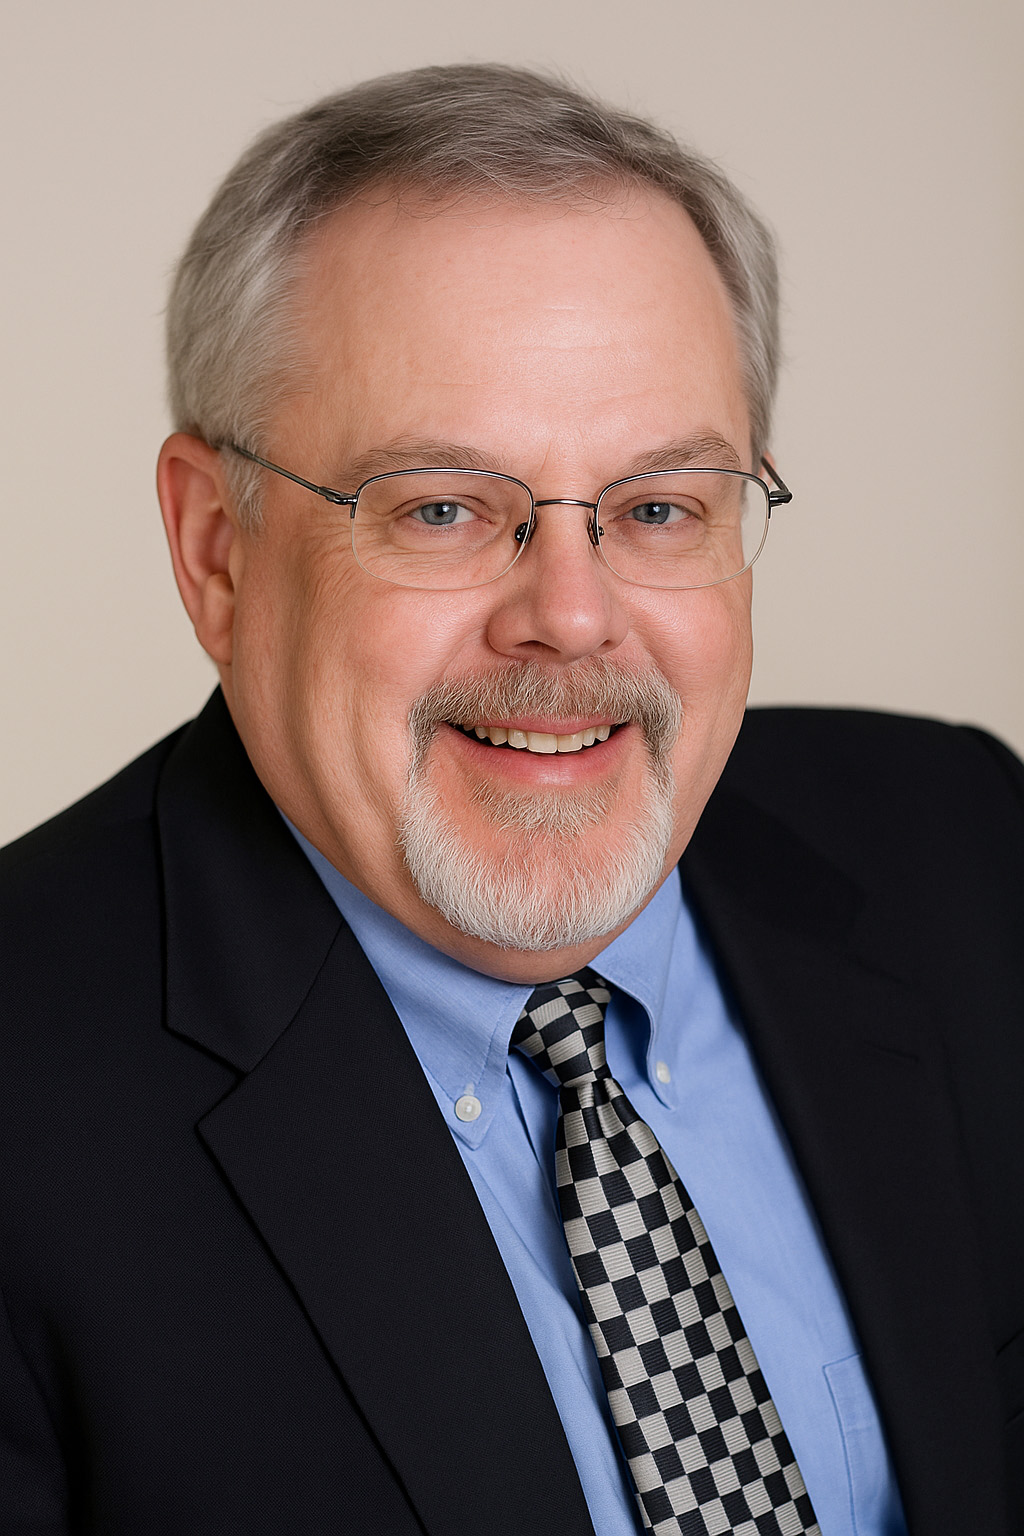
Del Heles
Del Heles is the founder and CEO of Pc Market Analysis (CMR), a channel administration software program firm he launched in 1984. With greater than 40 years of expertise, he’s recognized for serving to producers and distributors simplify advanced accomplice applications by means of sensible, customer-focused expertise options.